Coolify
Deploy OpenClaw on Coolify behind the open-source ControlClaw firewall. One Compose file, pasted as a new resource, makes the firewall OpenClaw's only way to the internet.
This guide runs OpenClaw on your Coolify server with the ControlClaw firewall in front of it. You paste one Compose file into Coolify, and it starts three services:
- firewall: the ControlClaw firewall, its panel and its proxy.
- egress: a small Alpine container that owns OpenClaw's network. Its packet filter drops everything except traffic to the firewall's proxy.
- openclaw: Coolify's own OpenClaw image, with its login page, running inside
egress's network.
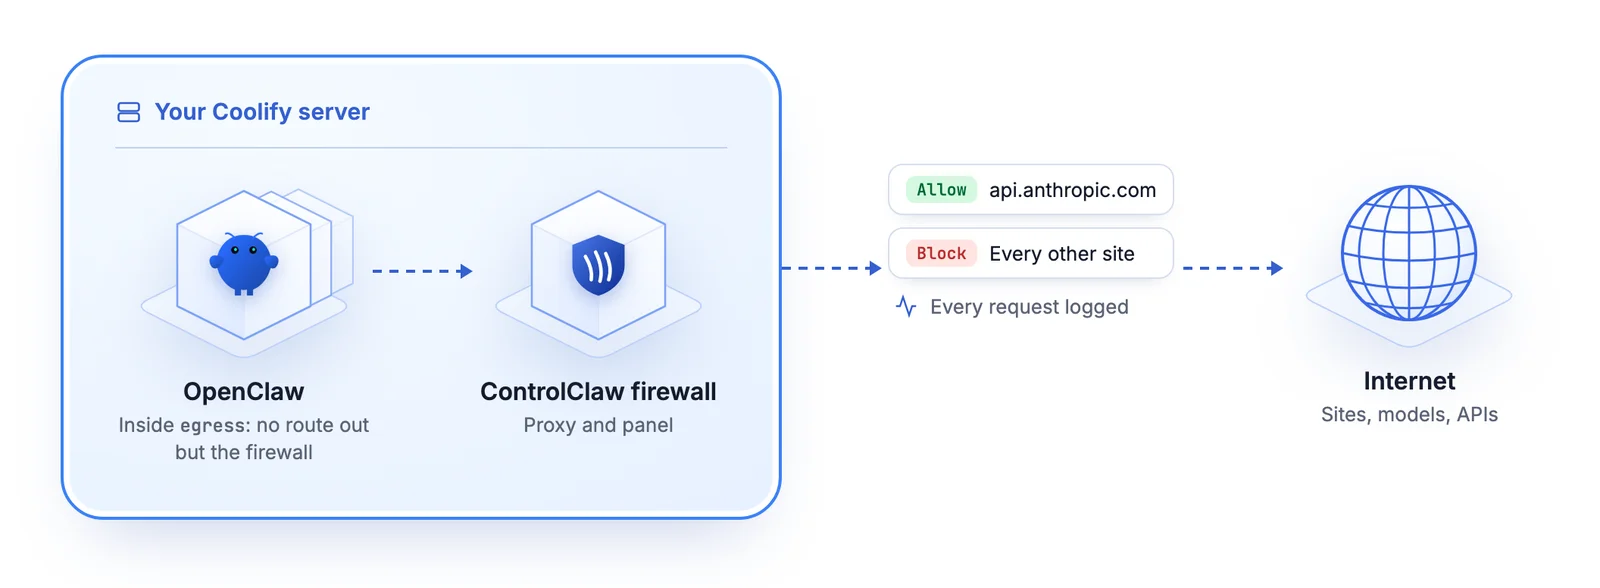
Coolify attaches its own network to every service in a Compose file. The packet filter lives in OpenClaw's network namespace, so that extra network doesn't give OpenClaw a way out. We tested this guide on Coolify 4.
What you need
- A Coolify server with 4 GB of RAM or more. The firewall uses about 200 MB.
- An API key for OpenClaw's model, such as Anthropic, OpenAI or OpenRouter. OpenClaw doesn't start without one.
Add a Docker Compose resource
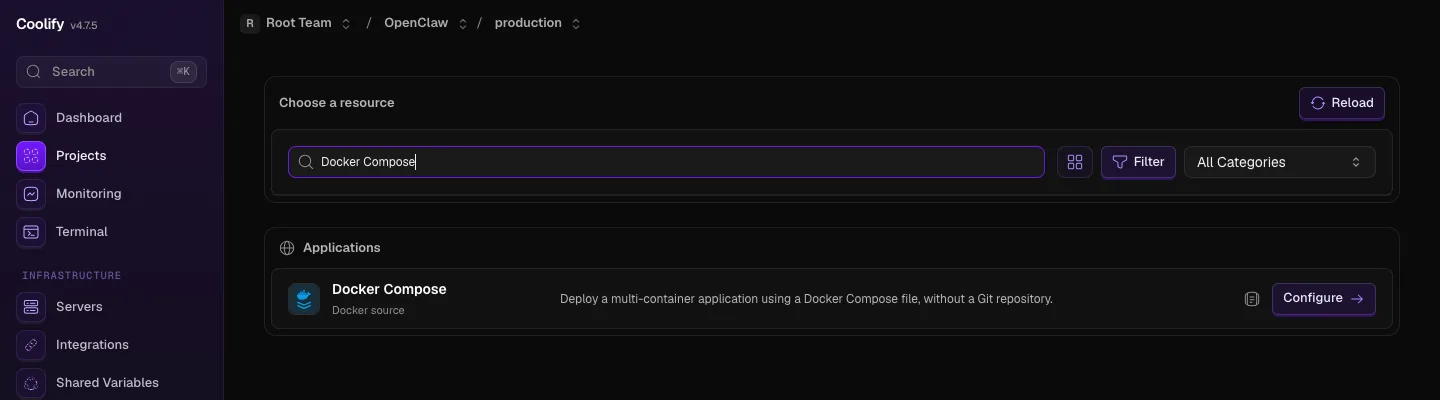
Open a project (or create one), click + New and search for Docker Compose. Choose Docker Compose, the one whose source is a Compose file, without a Git repository.
Paste the Compose file
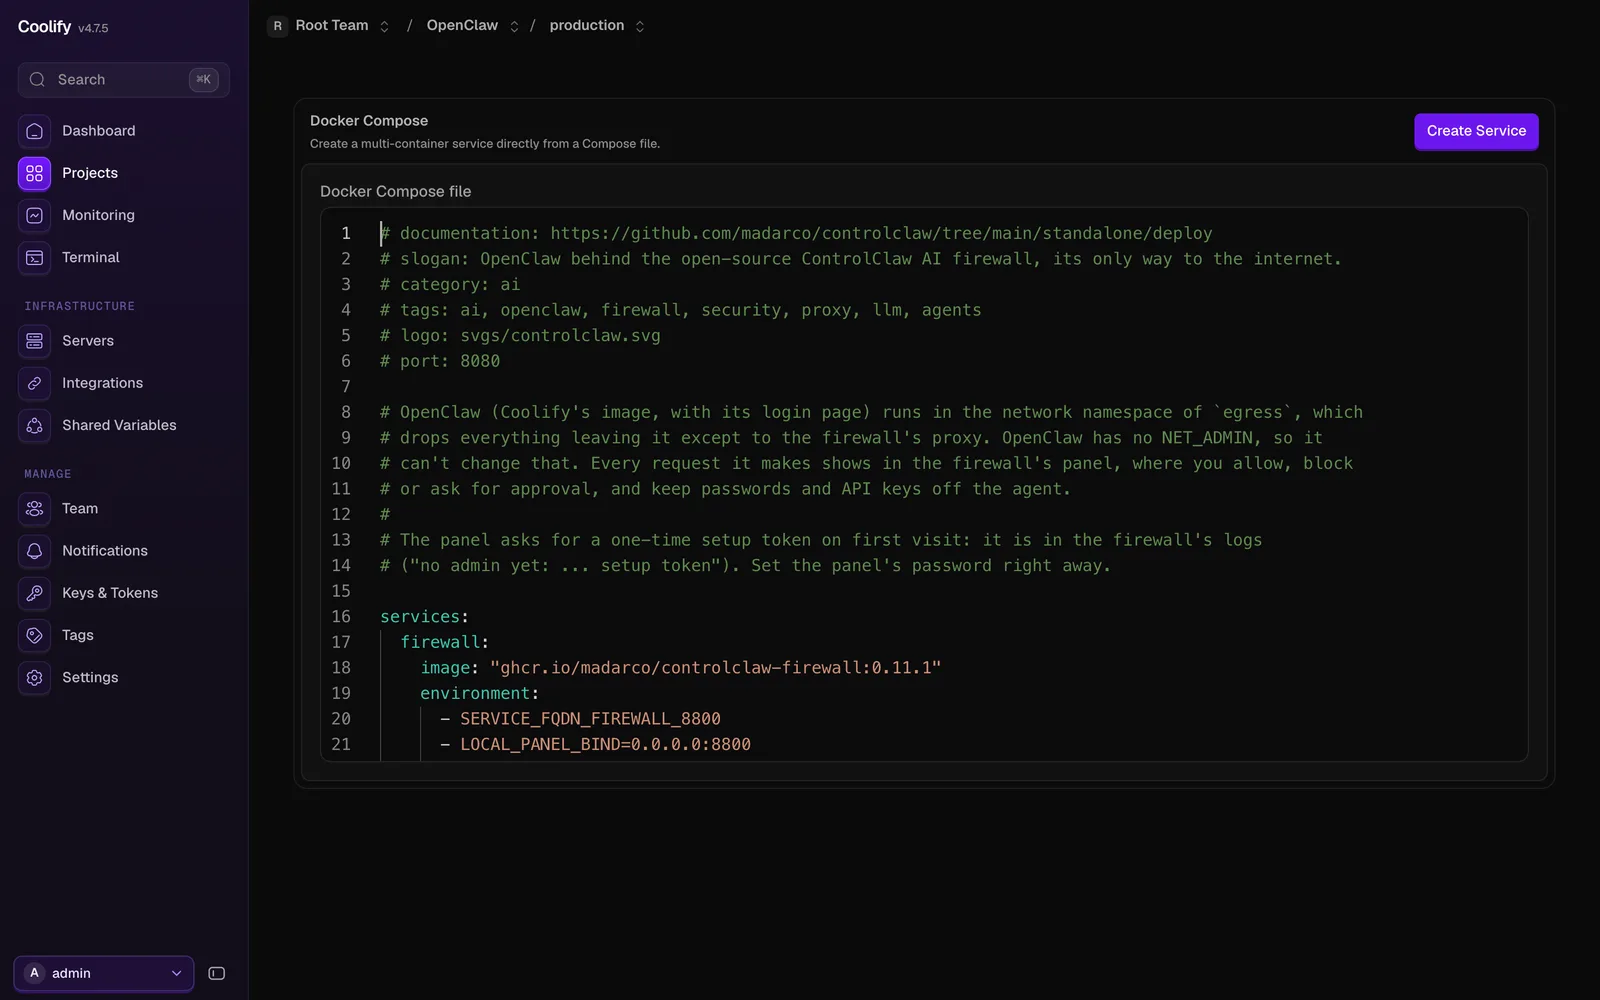
Copy the file from GitHub and paste it in the editor:
coolify/controlclaw-openclaw.yaml.
Click Create Service.
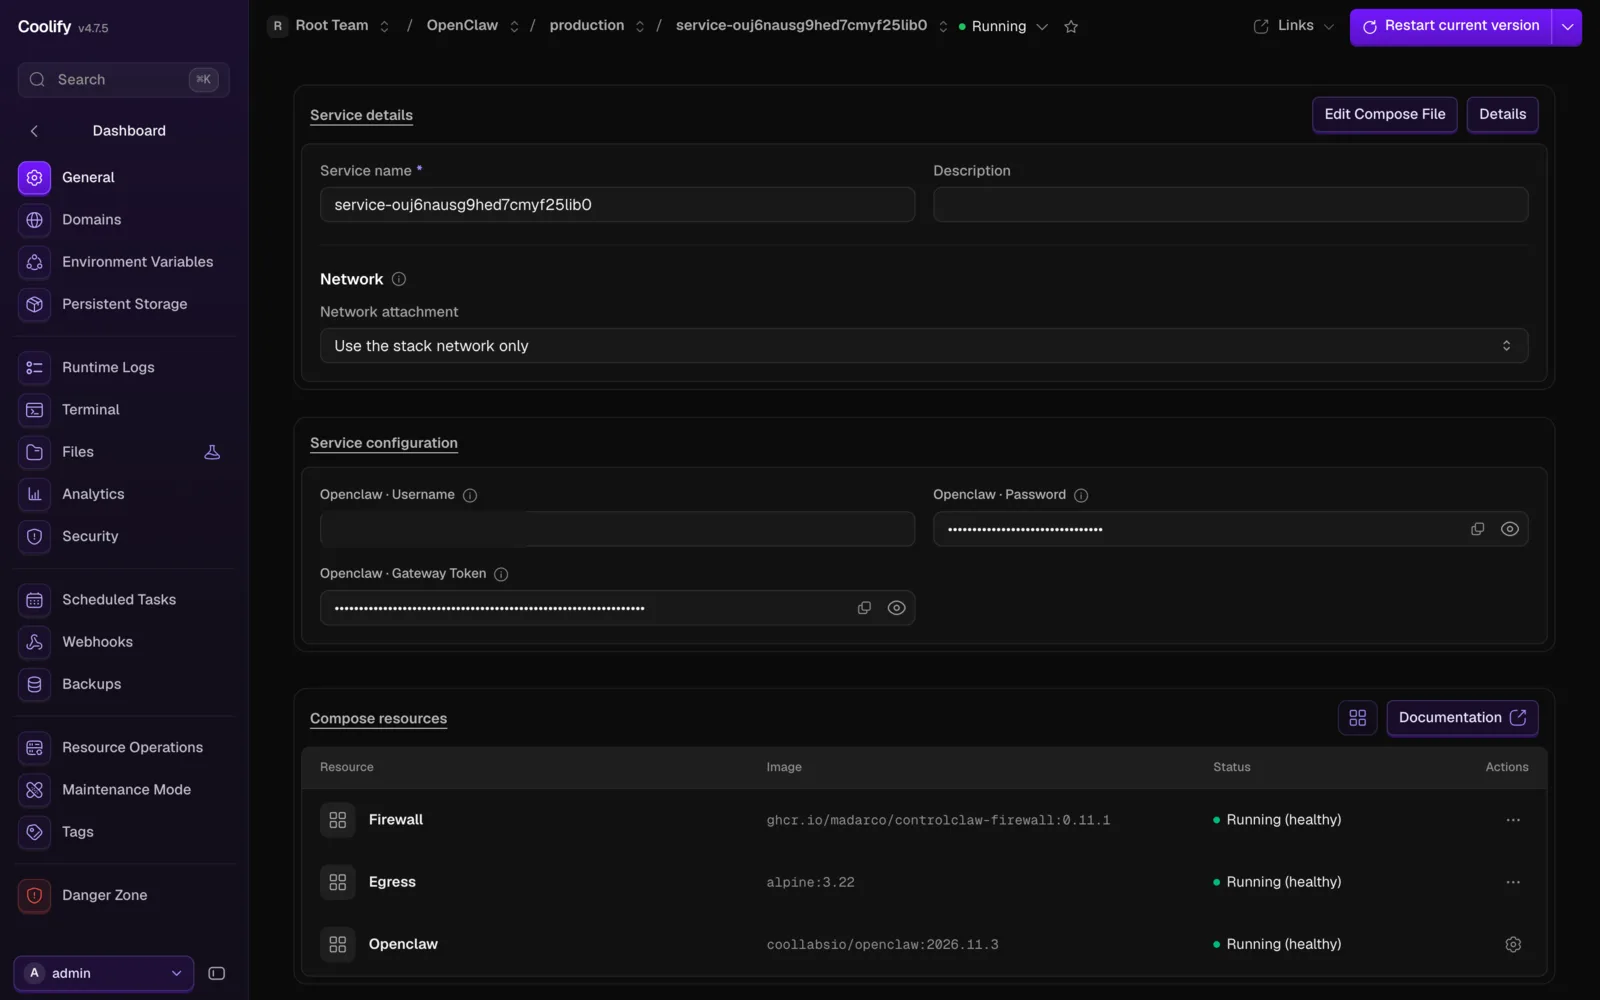
Coolify then shows the new service. It has made OpenClaw's login (username and password) and its gateway token for you. Keep them: you need them to open OpenClaw.
Switch the domains to HTTPS
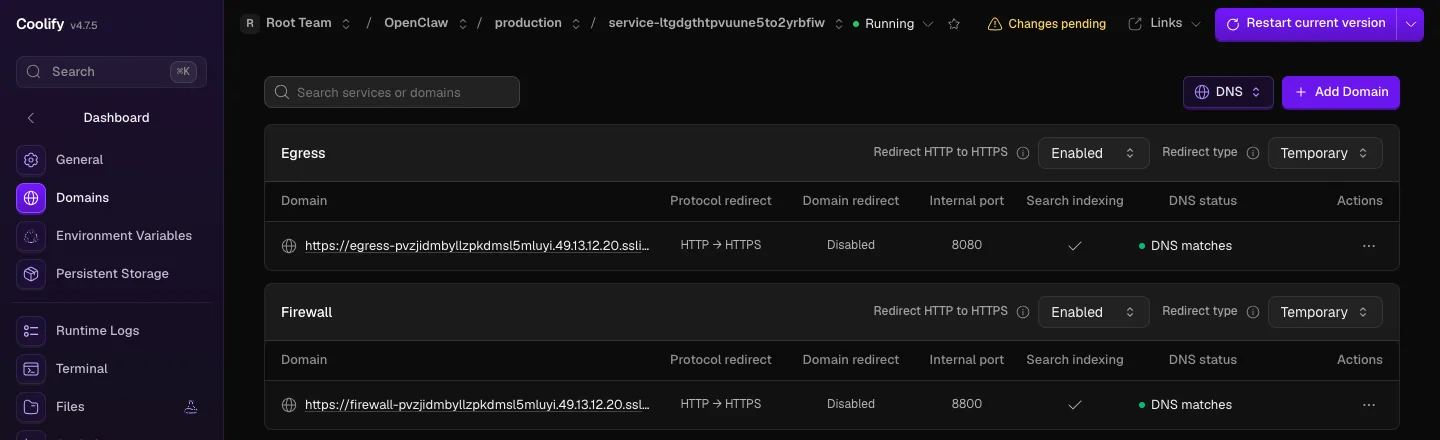
Under Domains, Coolify gives egress (OpenClaw's Control UI, port 8080) and firewall (the
panel, port 8800) a domain each. Change them to your own domains if you like. The file passes the
panel's domain to the firewall, which answers only under that name.
Edit each domain and set Protocol to https. Coolify then gets a certificate for it. The panel
only works over HTTPS: on a plain http:// domain, your browser drops its sign-in cookie and the
panel signs you out after every page.
Add a model key
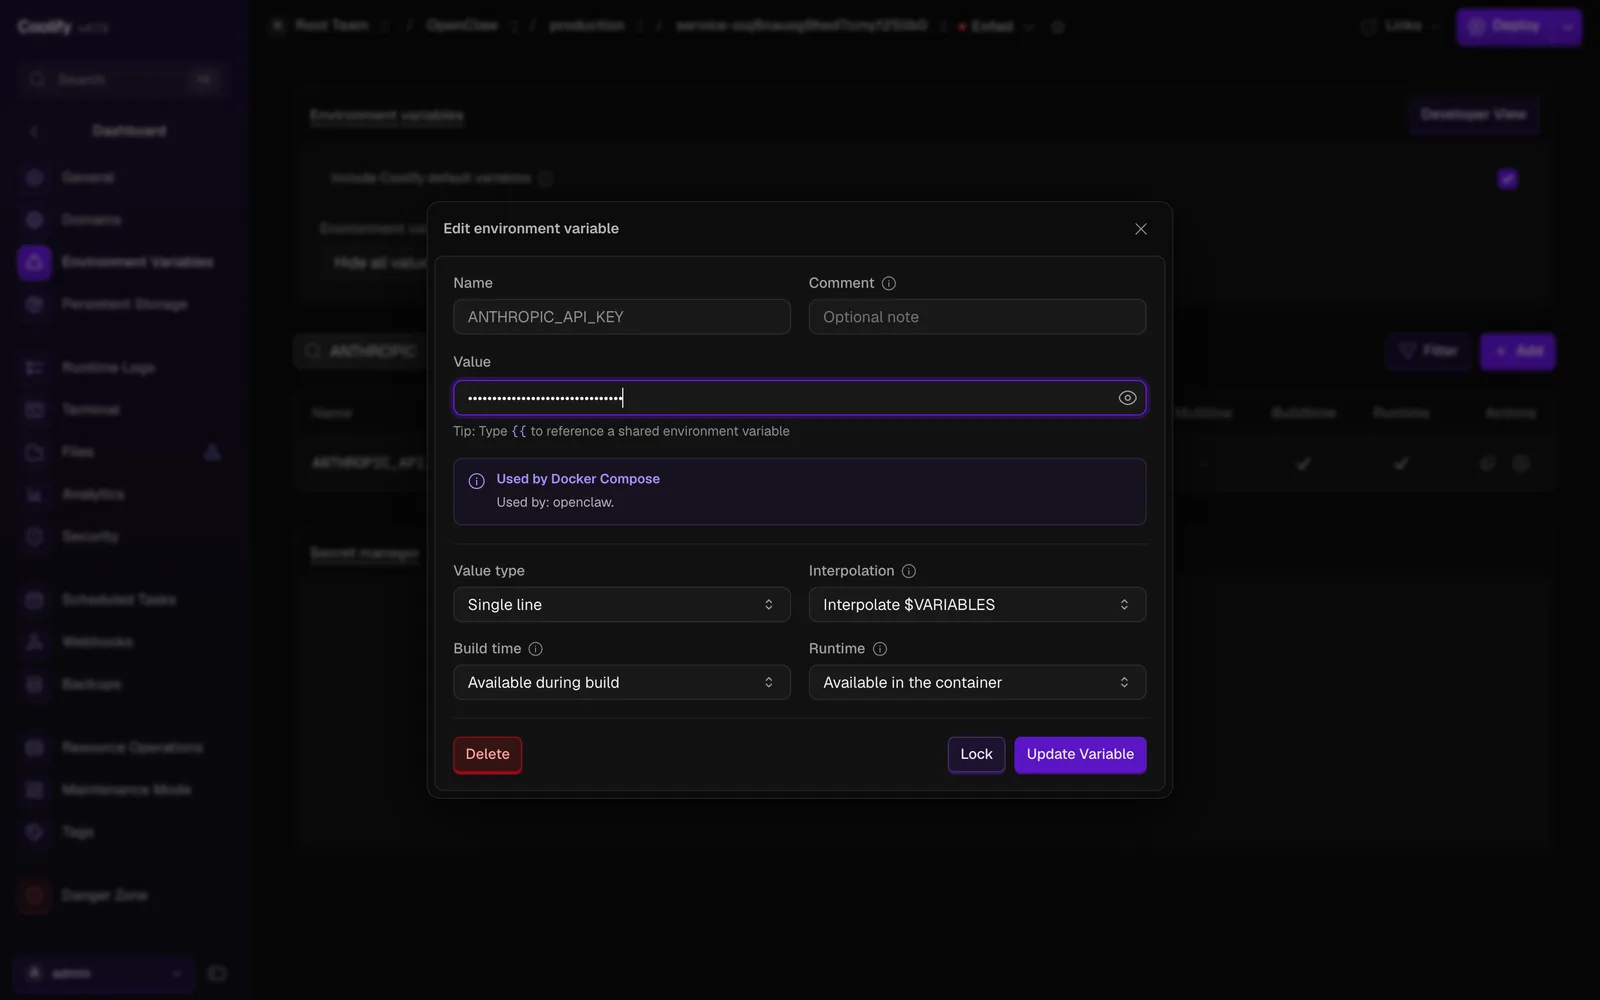
Open Environment Variables and set one of ANTHROPIC_API_KEY, OPENAI_API_KEY or
OPENROUTER_API_KEY. The others can stay empty.
The key goes in OpenClaw's environment here. The firewall can also keep model keys and add them to
requests on the way out, but only for an agent connected with controlclaw connect, which this
setup doesn't use.
Deploy
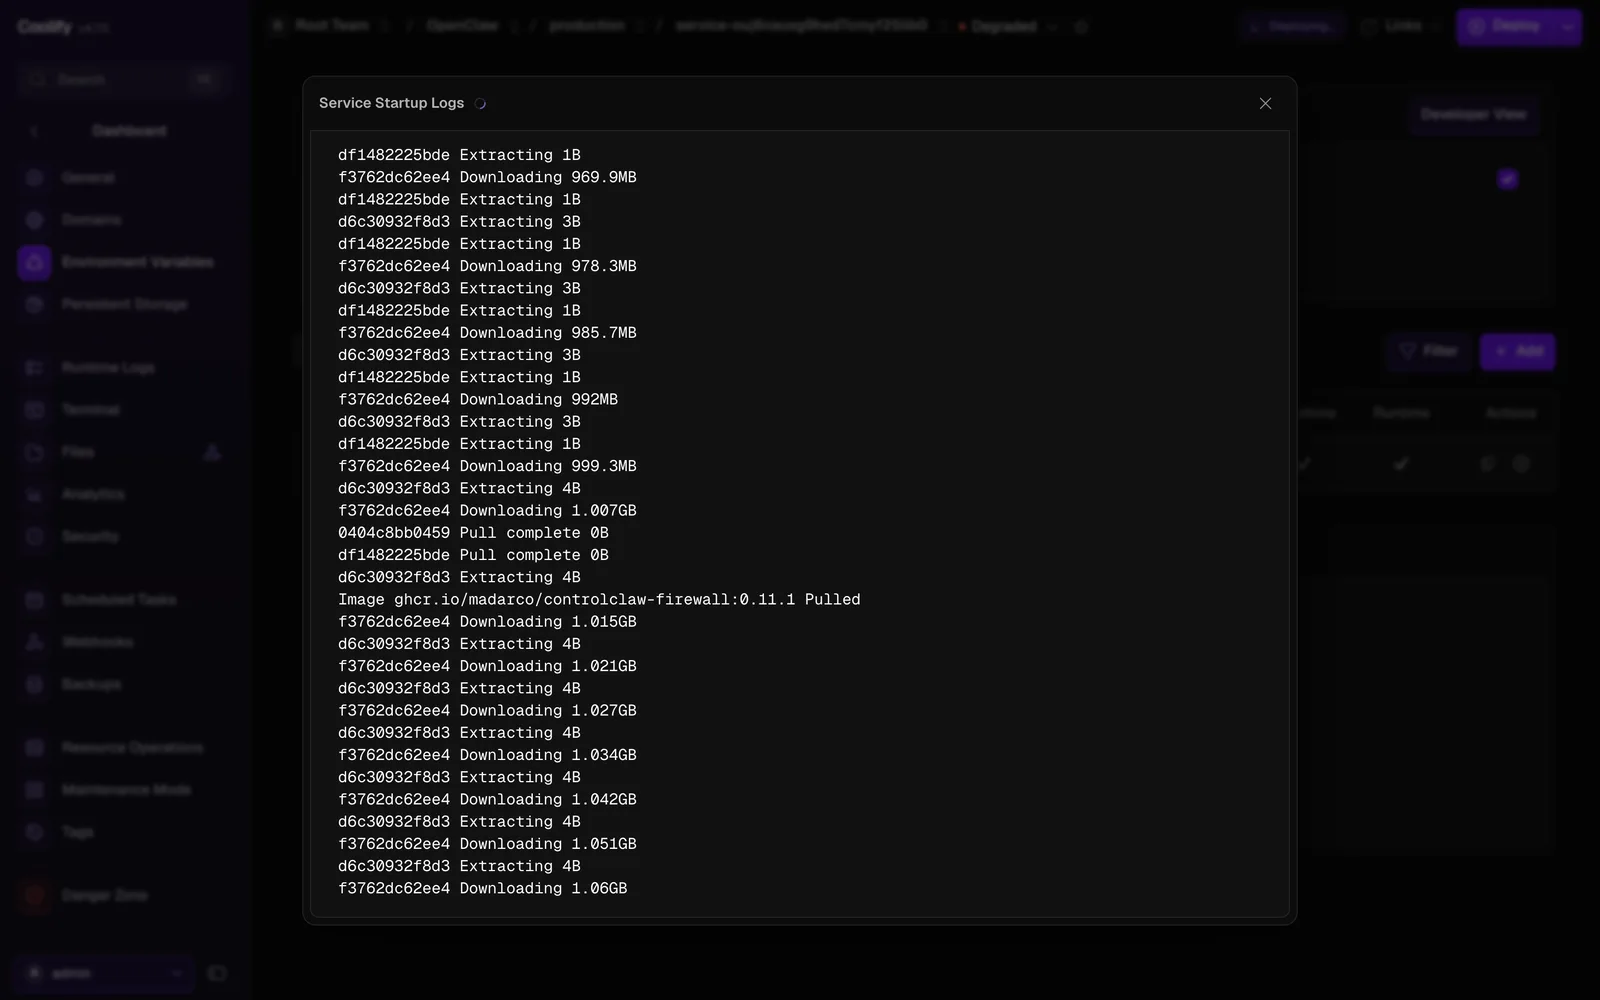
Click Deploy. The first start takes a few minutes while the images download. egress waits for
the firewall to be healthy, and OpenClaw waits for egress.
Open the panel
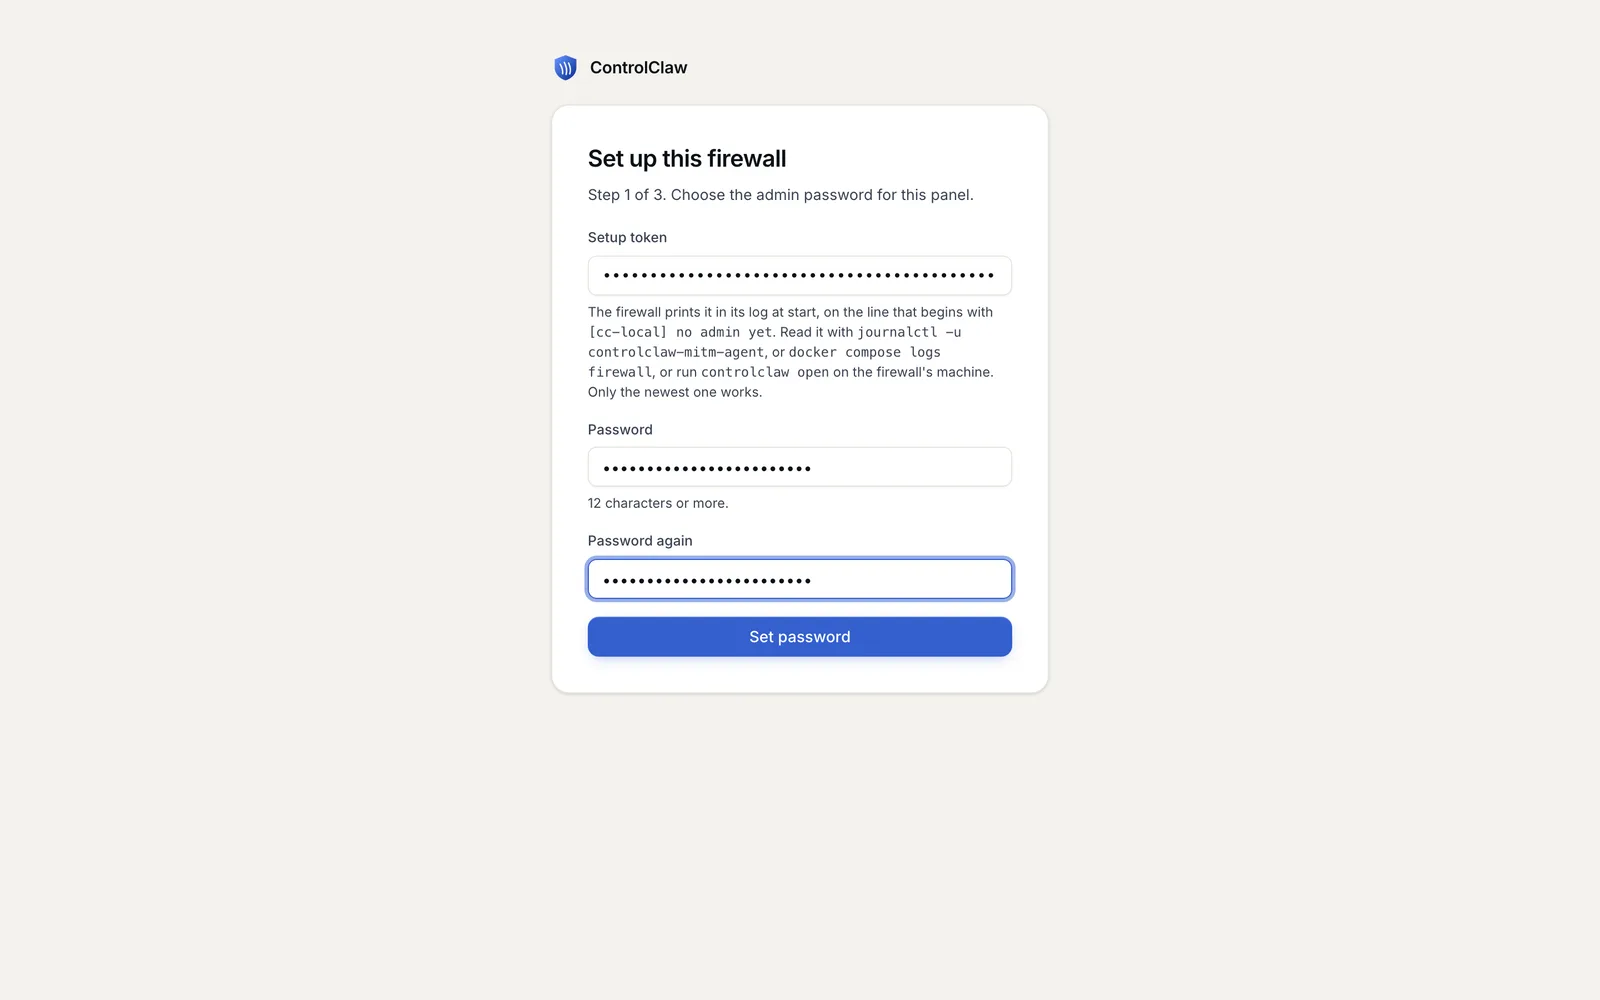
Open the firewall's domain. The panel asks for a one-time setup token. In Coolify, open the
Firewall resource's logs and find the line that starts with [cc-local] no admin yet. Paste the
token, and set the admin password right away: until you do, anyone who can read the log can set it.
Open OpenClaw
Open the egress domain and sign in with the username and password from the service page. Then
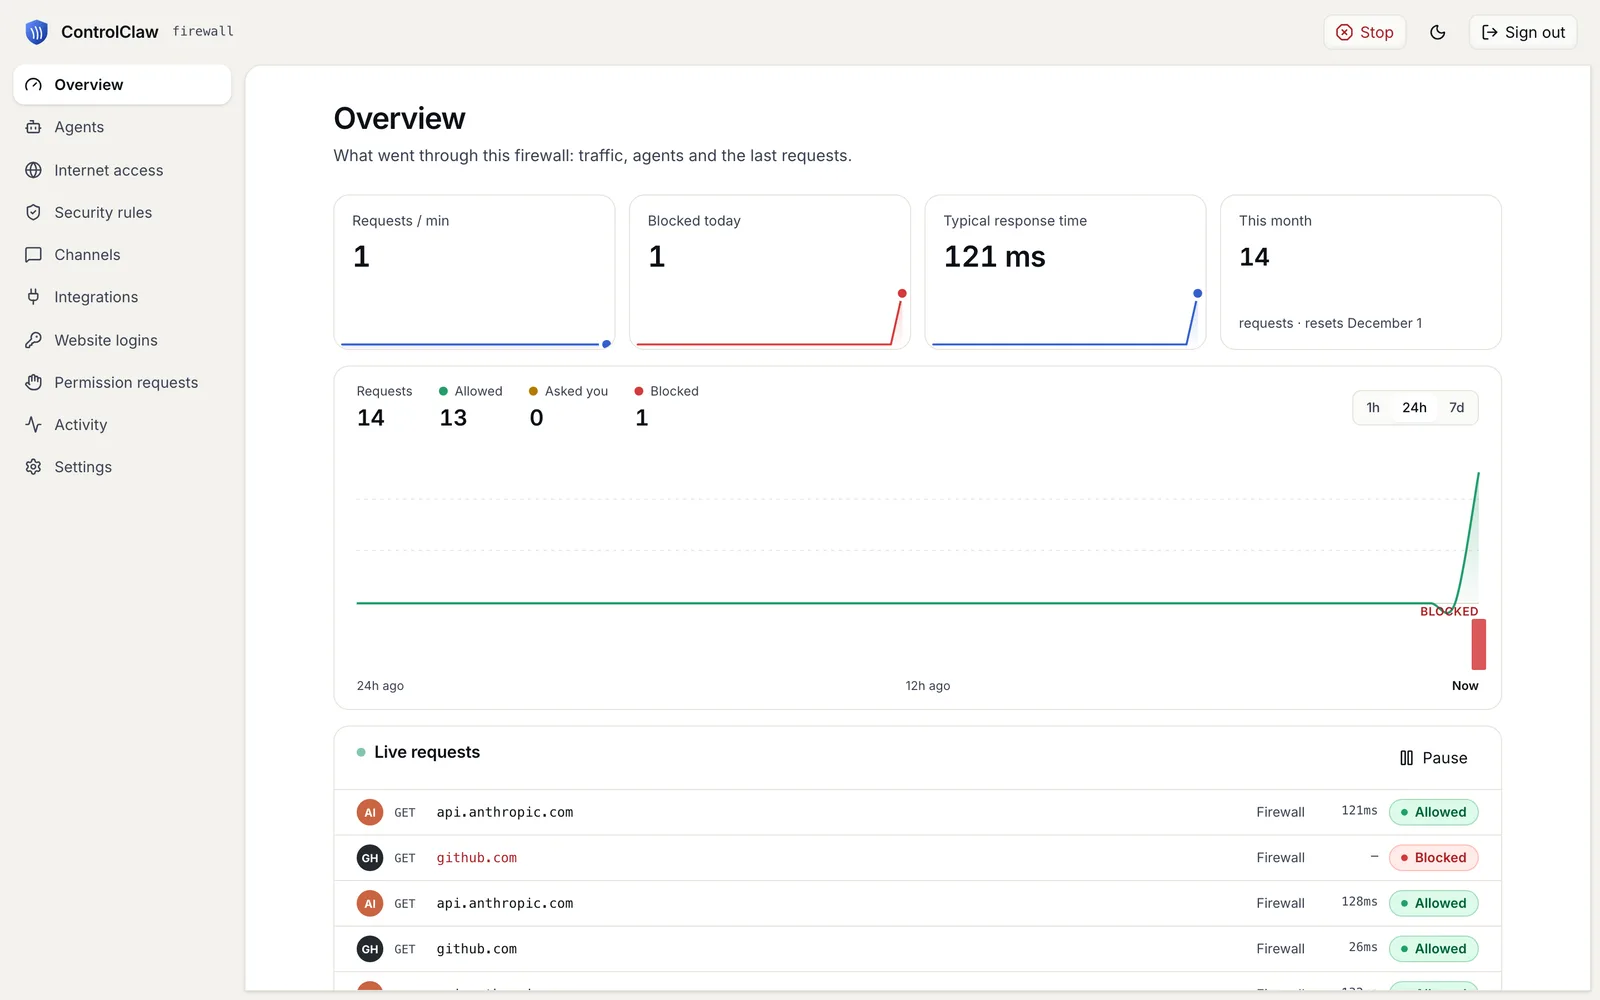
ask OpenClaw something that needs the web. The request shows on the panel's Overview and in
Activity. OpenClaw's requests show under the agent Firewall.
Lock it down
A new firewall allows every site and logs it. In the panel, open Internet access and set
Every other site to Block. Then allow your model provider's host, for example
api.anthropic.com, or OpenClaw can't reach its model.
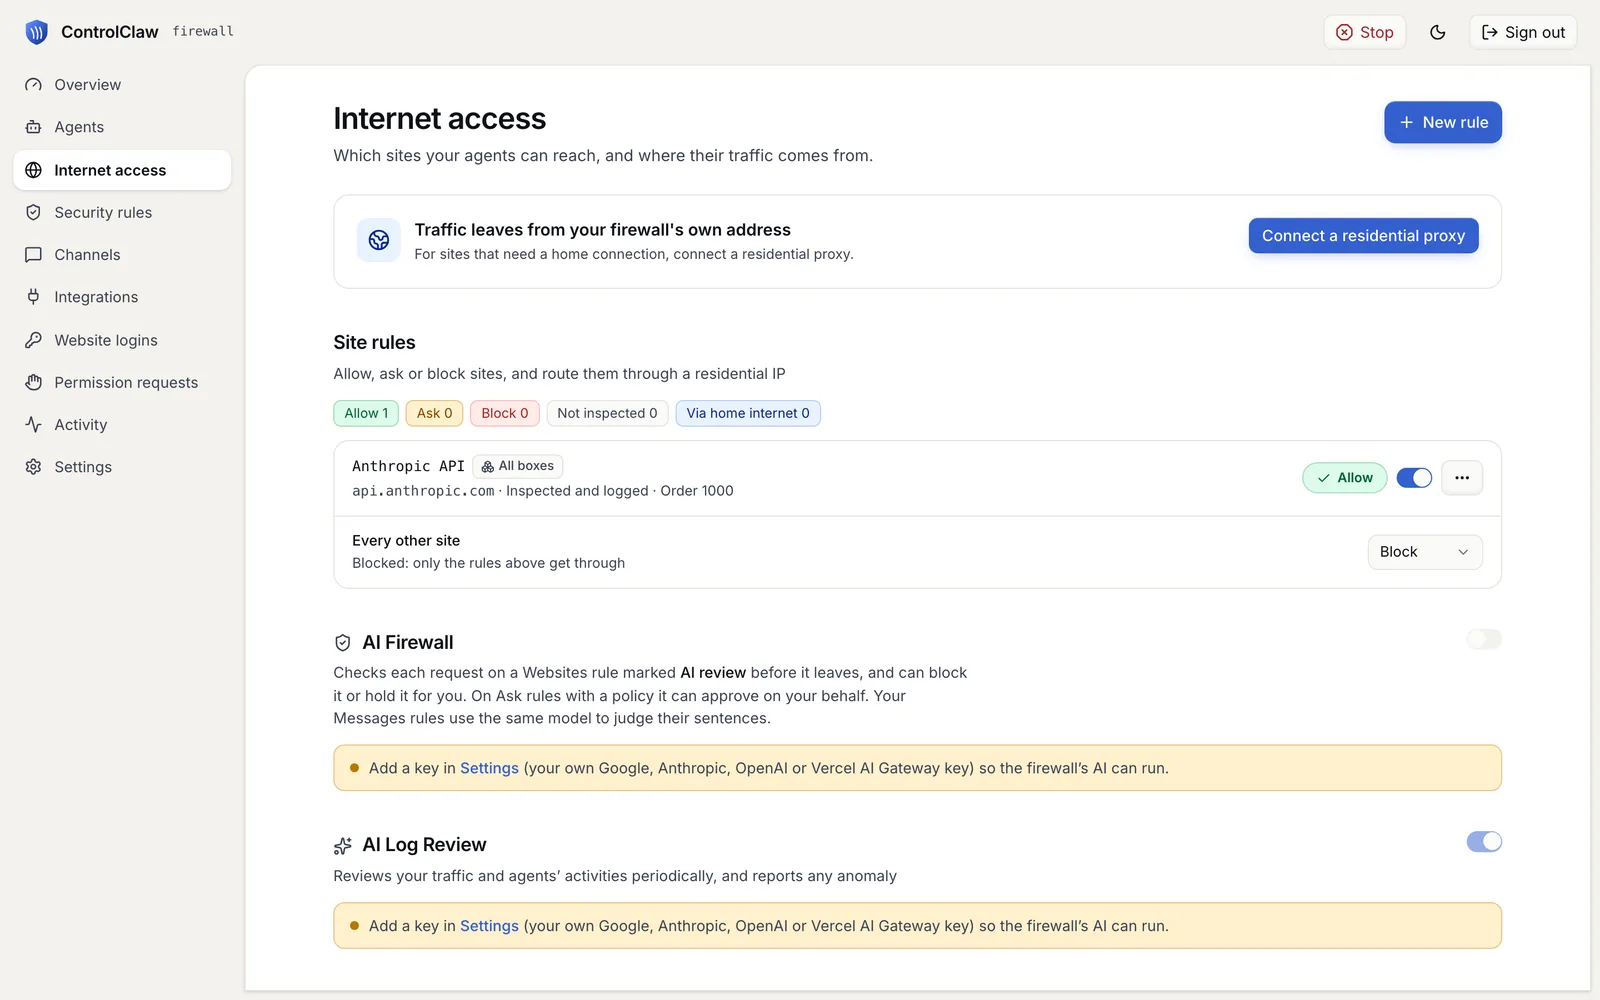
In the Overview above, github.com was blocked by this rule, and OpenClaw's request to its model
still went through.
What this setup can't do
Compared with npx controlclaw up --all on a plain server:
- The panel can't set OpenClaw's model or bots, or stop it.
- OpenClaw's requests show without an agent name, so rules and secrets for one named agent don't apply to it. Rules for every agent do.
- There's no browser container. Coolify's own OpenClaw template has one; this file leaves it out.
Remove it
Delete the service in Coolify and tick the option to delete its volumes. That deletes the firewall's certificate authority and every secret it holds.
Docker Compose
Run OpenClaw behind the ControlClaw firewall with one Docker Compose file. OpenClaw can reach the internet only through the firewall.
Dokploy
Deploy OpenClaw on Dokploy behind the open-source ControlClaw firewall. Import one template, add a model key and deploy. The firewall is OpenClaw's only way to the internet.